Integrate Delinea Secret Server with an Entrust nShield HSM
There are two cryptography API options for this integration: the CNG cryptography provider, and the PKCS #11. Both are covered in this section.
Configure the Delinea Secret Server using the CNG cryptography provider
-
Select Windows Start > Entrust nShield Security World > CNG configuration wizard. The nShield CNG Providers Configuration Wizard appears.
-
Select Next twice.
-
Select Use the existing security world if one was created in Create a Security World.
-
Select Next twice.
-
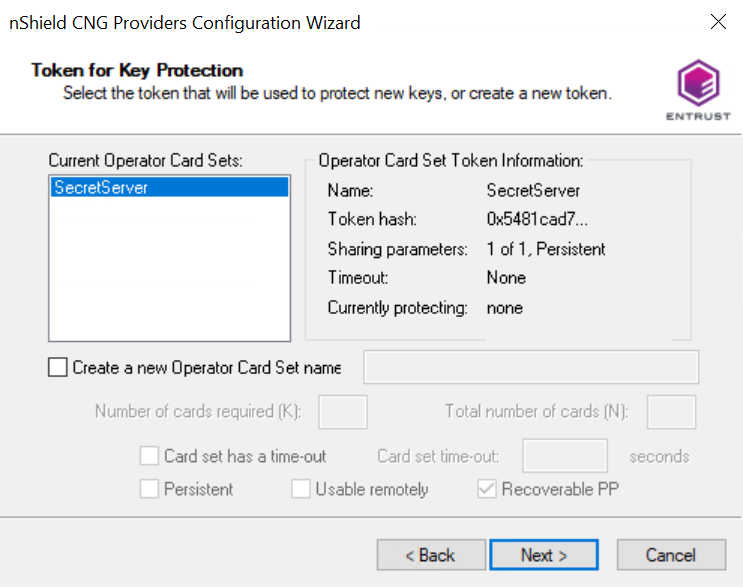
Select the protection method. If you are using OCS protection, insert your OCS card into the proper slot and then select Next.
Example for OCS protection:
-
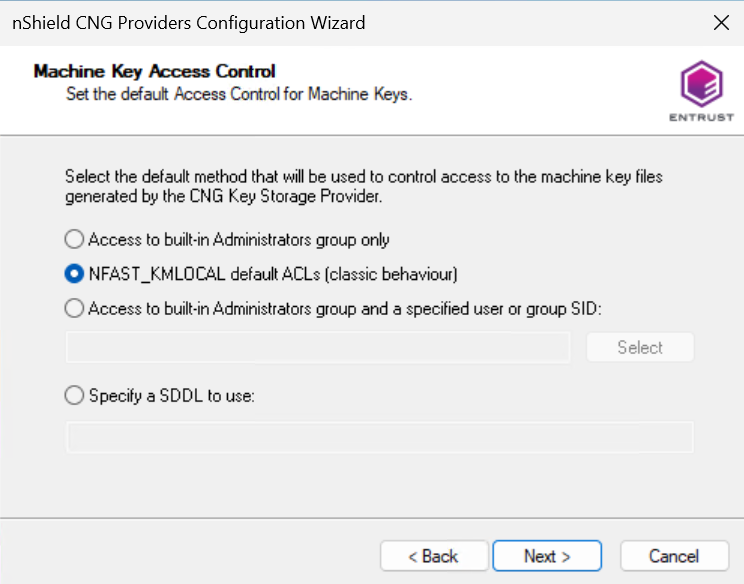
If the Machine Key Access Control window appears, select the option that best meets your security and operational requirements and specify the service account used by the Secret Server, then select Next.
For example:
-
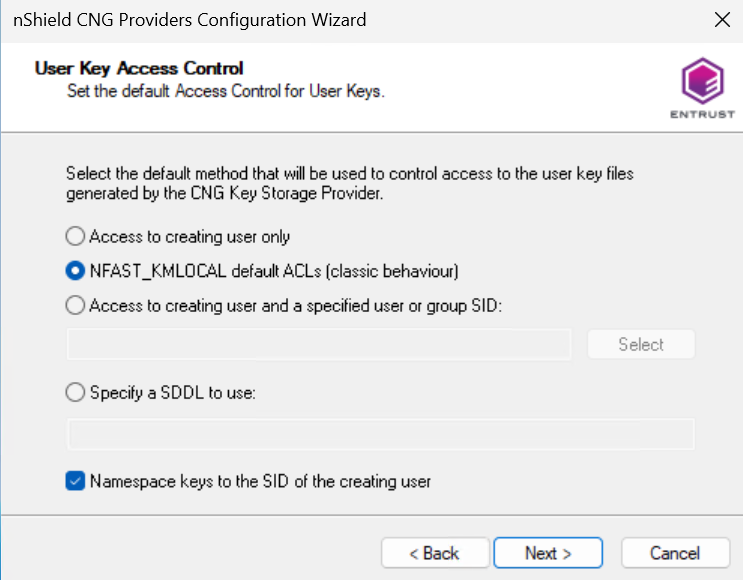
If the User Key Access Control window appears, select the option that best meets your security and operational requirements and ensure that the Namespace keys to the SID of the creating user remains selected, then select Next.
For example:
-
Select Next and Finish.
-
Run
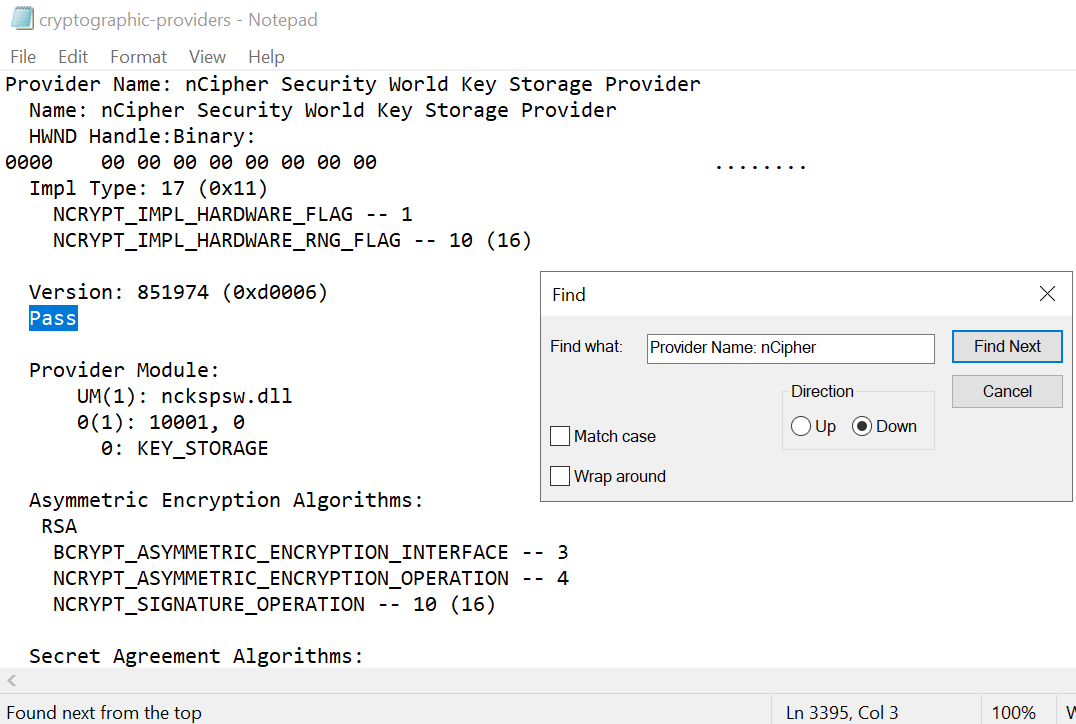
certutil -csptest > <filename>on a command window.For example:
C:\Users\Administrator.INTEROP>certutil -csptest > Documents\cryptographic-providers -
Search for Provider Name: nCipher in the file created above, and make sure that it shows Pass.
-
Log in to the Delinea Secret Server via a browser at https://localhost/SecretServer.
-
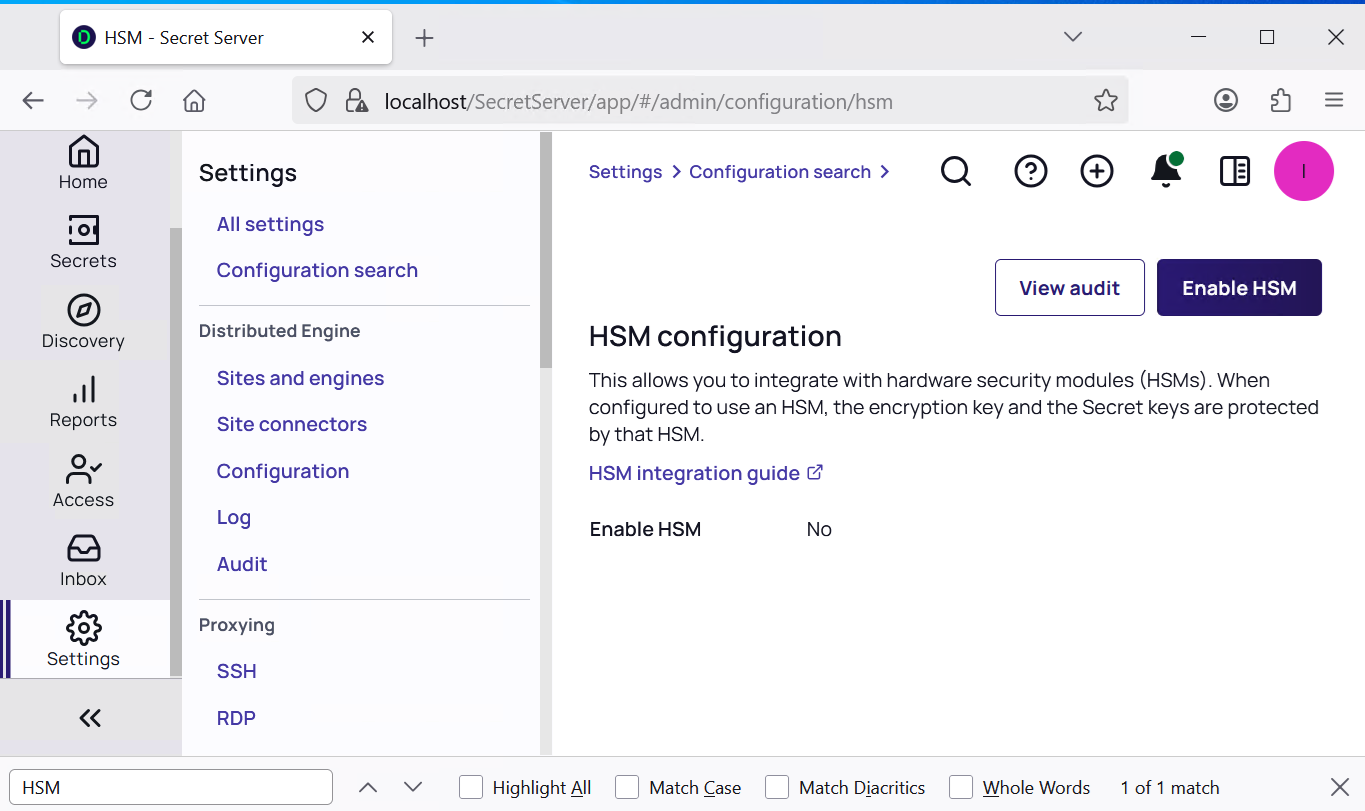
From the menu in the left pane, select Settings > All settings > Configuration > General > HSM. The HSM configuration page appears.
-
Select Enable HSM, then select Next.
-
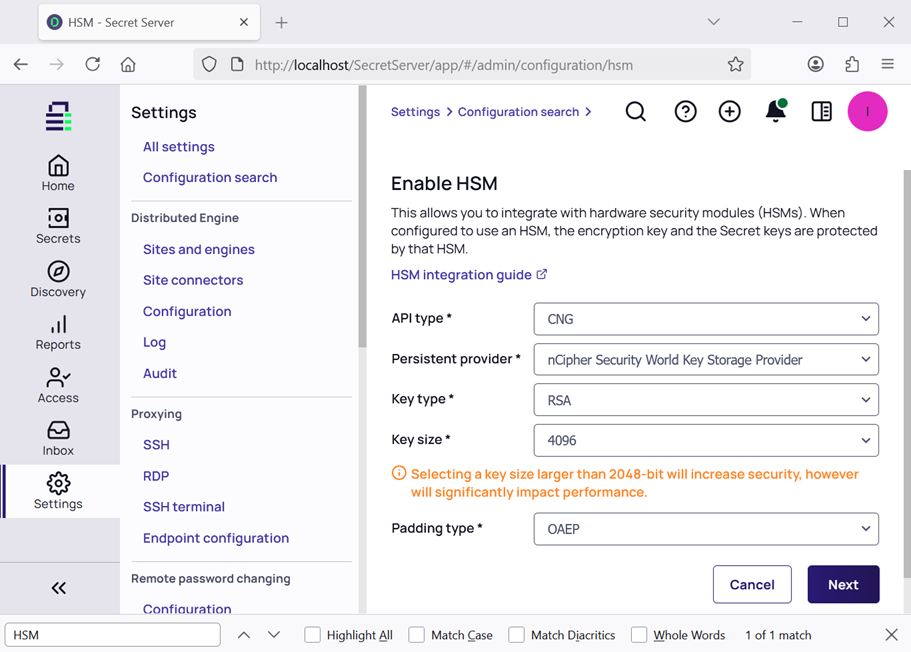
In the Enable HSM window, select as follows, then select Next.
Parameter Value API type
Select CNG
Persistent provider
Select nCipher Security World Key Storage Provider
Key type
Select the required value
Key size
Select the required value
Padding type
Select the required value
For example:
-
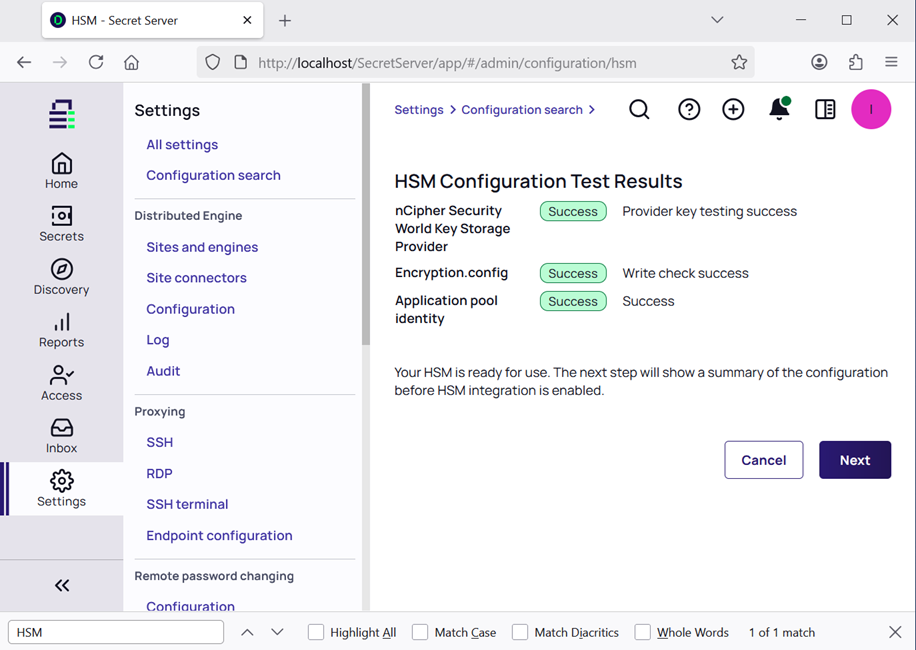
Check the HSM Provider Test Results, then select Next.
-
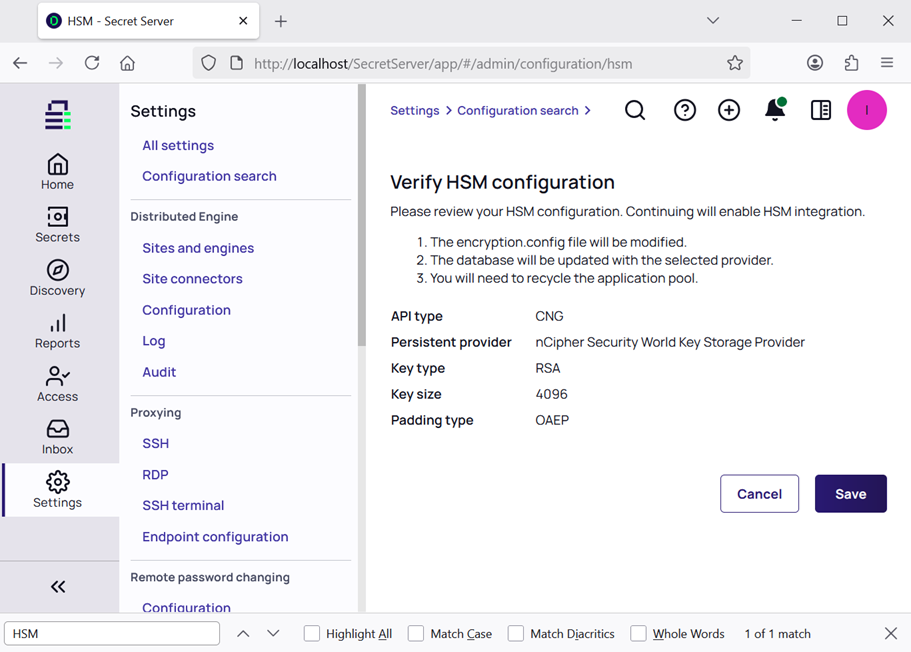
In the Verify HSM configuration page select Save.
-
In the Notice about HSM configuration change, recycle the application pool and then select Continue.
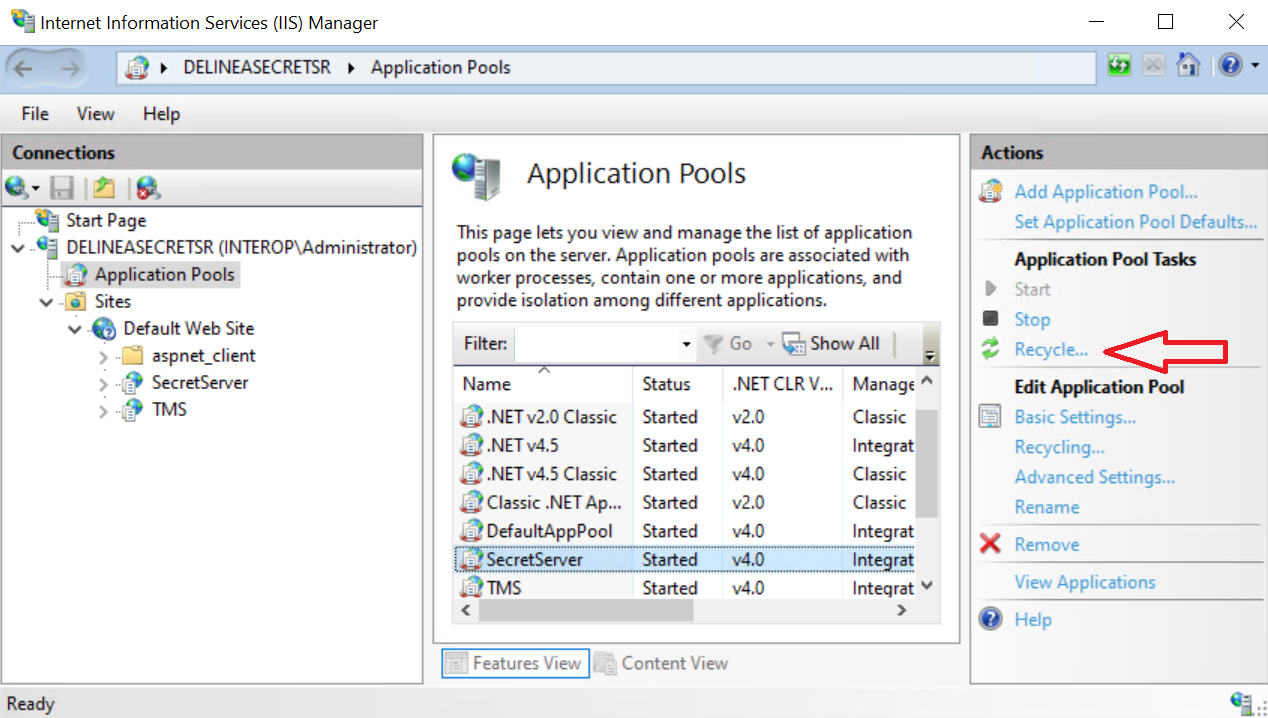
-
Refresh the browser. Then from the menu in the left pane, select Settings > All settings > Configuration > General > HSM. Notice the completed HSM configuration.
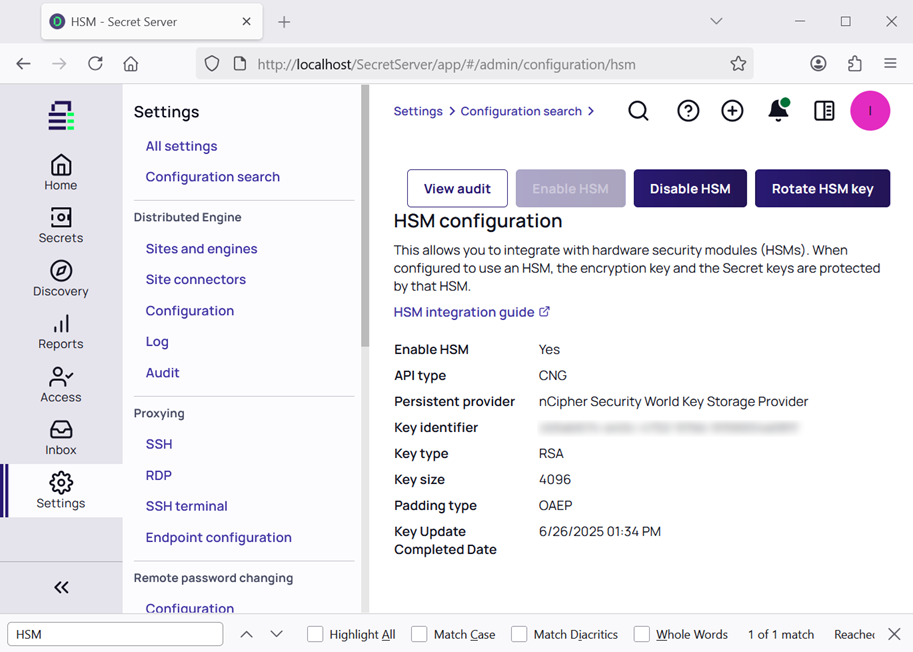
Configure the Delinea Secret Server using the PKCS #11 API
-
Log in to the Delinea Secret Server via a browser at https://localhost/SecretServer.
-
Copy the HSM
cryptokilibrary (dll) for PKCS #11 to the Secret Sever application pool as shown:C:\Users\Administrator.INTEROP>mkdir C:\inetpub\wwwroot\SecretServer\pkcs11 C:\Users\Administrator.INTEROP>copy "C:\Program Files\nCipher\nfast\toolkits\pkcs11\cknfast.dll" C:\inetpub\wwwroot\SecretServer\pkcs11\. 1 file(s) copied. -
If you are using OCS protection, insert your OCS card into the proper slot.
-
From the menu in the left pane, select Settings > All settings > Configuration > General > HSM. The HSM configuration page appears.
-
Select Enable HSM, then select Next.
-
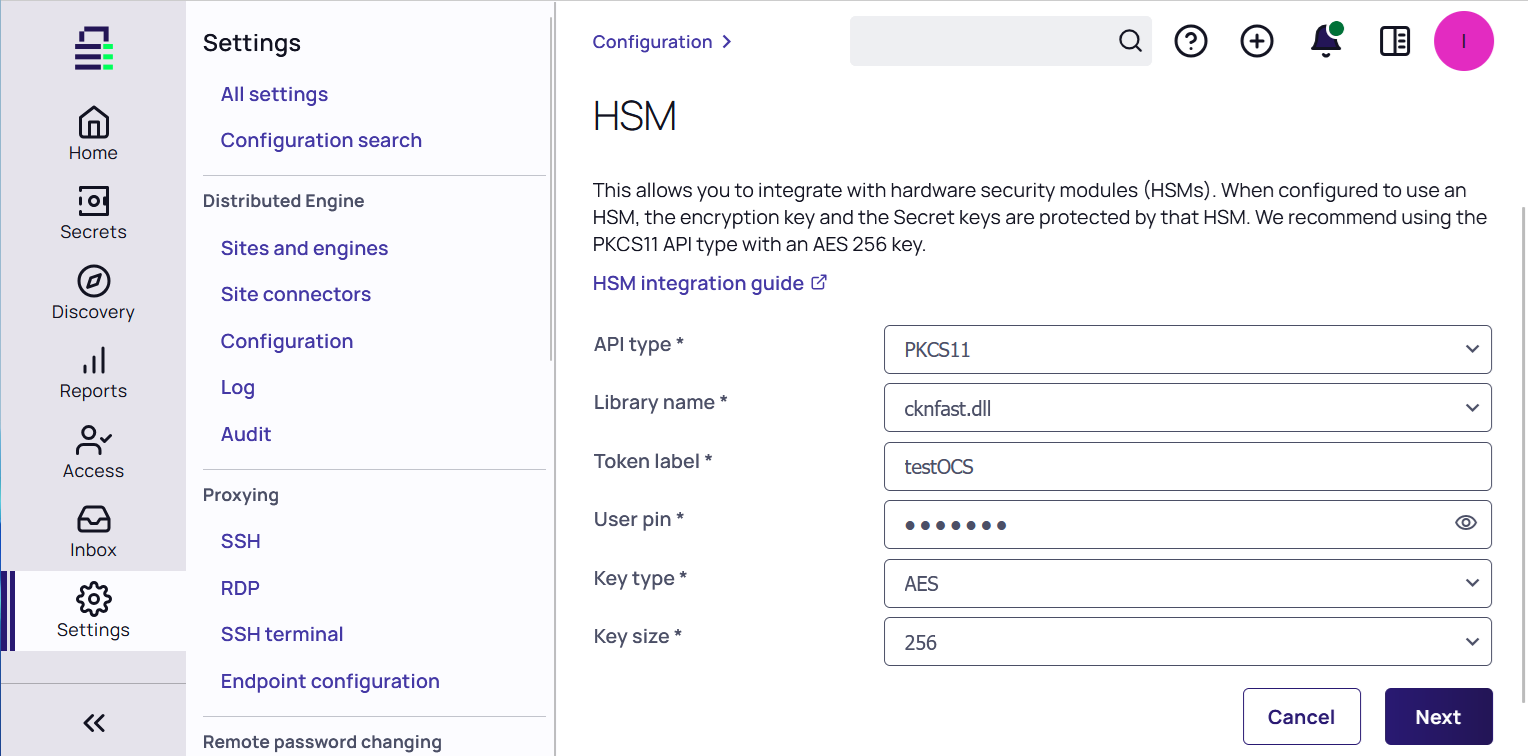
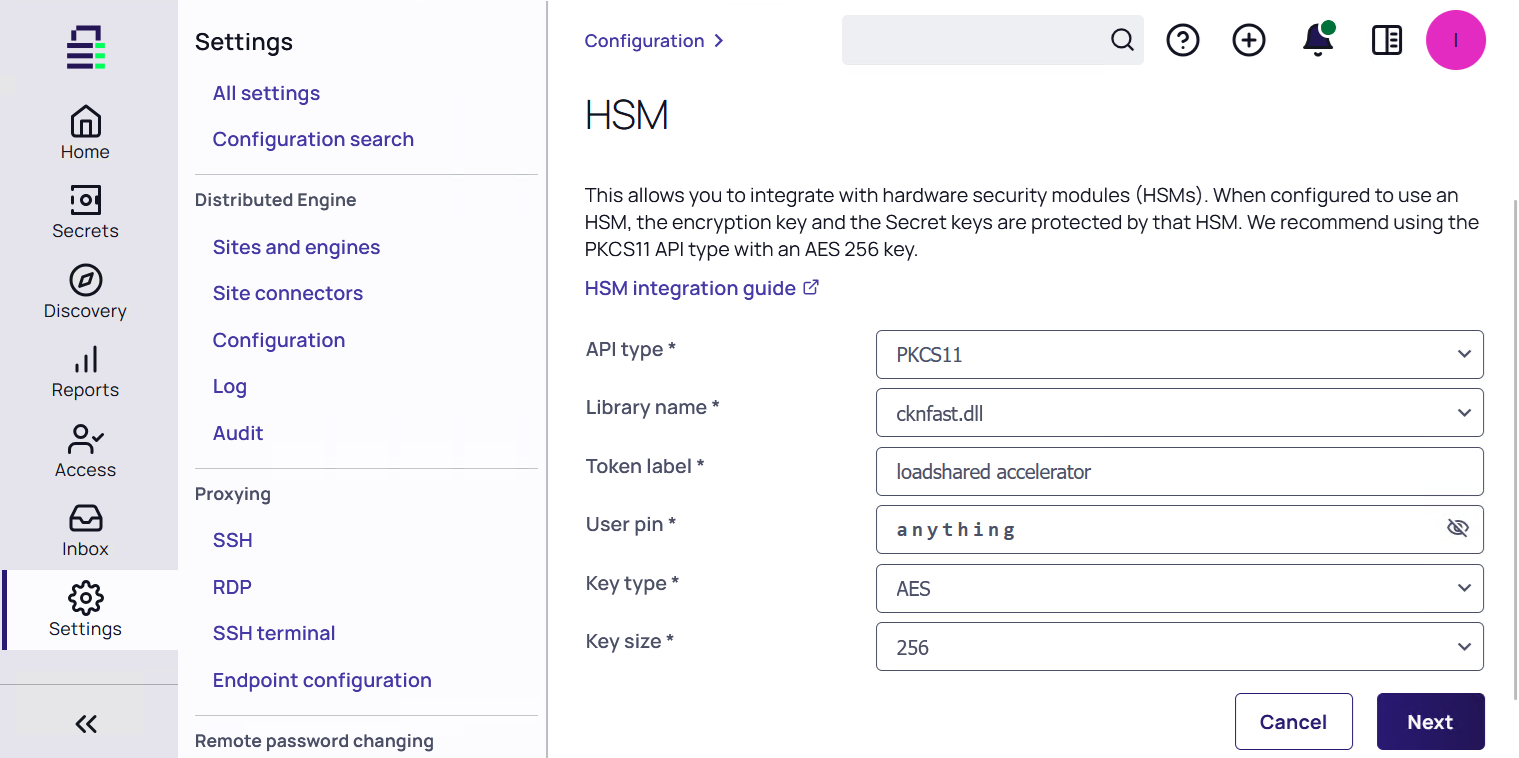
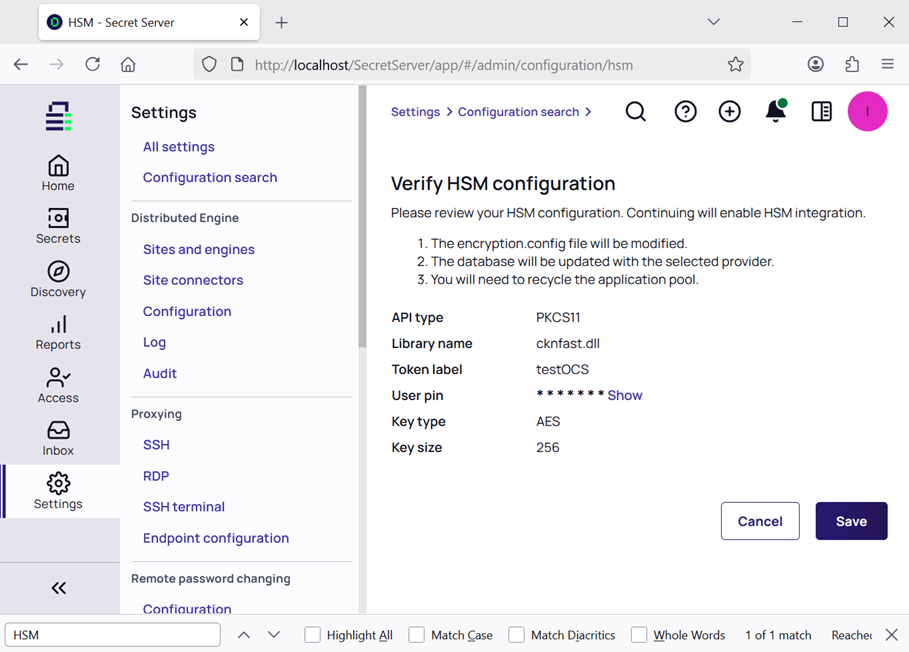
In the Enable HSM window, complete the fields as follows, then select Next.
Parameter Value API type
Select PKCS11
Library name
Select cknfast.dll
Token label
Enter the token name
User pin
Enter the token passphrase
Key type
Select the required value
Key size
Select the required value
Example with OCS protection:
Example with module-only protection:
-
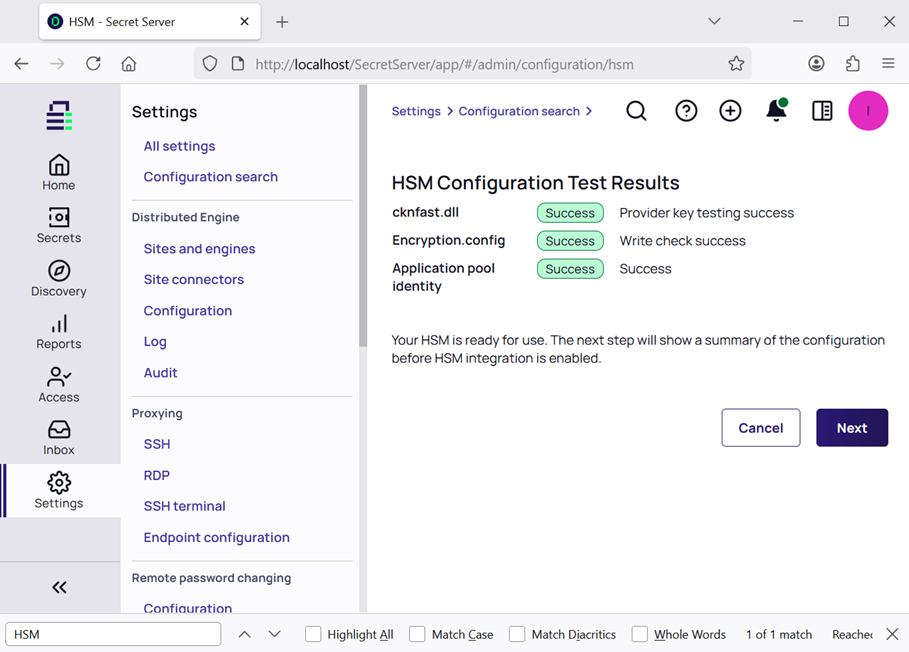
Check the HSM Provider Test Results, then select Next.
-
In the Verify HSM configuration page select Save.
-
In the Notice about HSM configuration change, recycle the application pool and then select Continue.
-
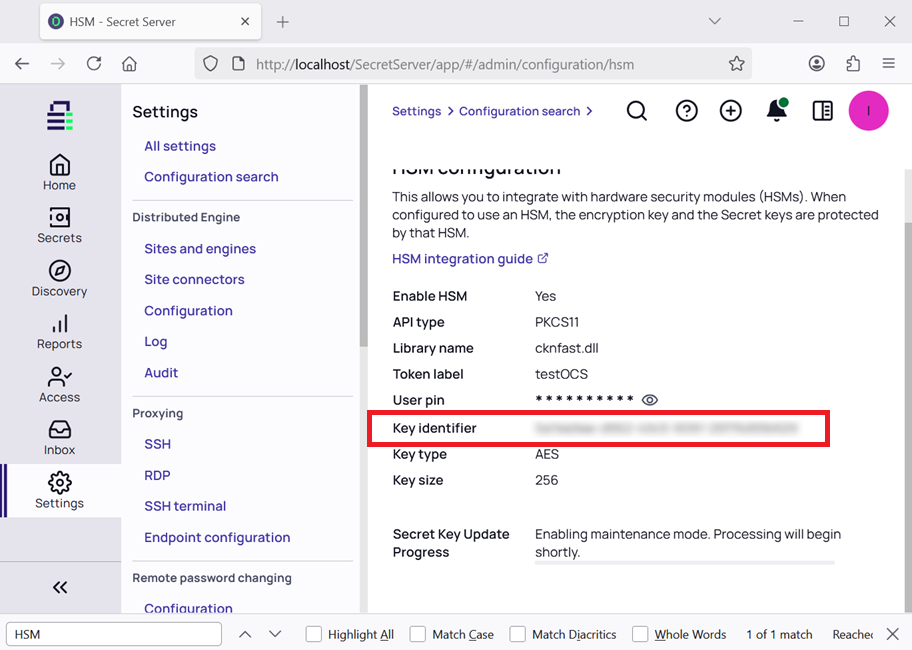
Refresh the browser. Then from the menu in the left pane, select Settings > All settings > Configuration > General > HSM. Notice the completed HSM configuration.
Verify integration
-
List the keys protected by the HSM using the
nfkminfoandrocsutilities.
For example:-
A key using the CNG cryptography provider:
C:\Users\Administrator.INTEROP>nfkminfo -l Keys protected by cardsets: key_caping_s-1-5-21-113020180-2446387811-180773374-1216--0d2944734a6e884bebffa501ccf26757dc717596 `f1291c9c-ec56-4c5e-a224-4aca528fceb2' C:\Users\Administrator.INTEROP>rocs `rocs' key recovery tool Useful commands: `help', `help intro', `quit'. rocs> list keys No. Name App Protected by 1 f1291c9c-ec56-4c5e-a224- caping testOCSnopassphrase rocs> quit -
A key using the PKCS #11 API:
C:\Users\Administrator.INTEROP>nfkminfo -l

Keys protected by cardsets:
 key_pkcs11_ucedb3d45a28e5a6b22b033684ce589d9e198272c2-7138a95db0d16a7e8cbe97e4ac6e201002e33b73 `fa3295f1-abd8-4030-a871-6fd87fefa172'

C:\Users\Administrator.INTEROP>rocs
`rocs' key recovery tool
Useful commands: `help', `help intro', `quit'.
rocs> list keys
  No. Name                     App        Protected by
    1 fa3295f1-abd8-4030-a871- pkcs11     testOCS
rocs> exit
-
-
Notice the Key identifier in the completed HSM configuration matches the
nfkminfoutility output above.
This completes the integration of Delinea Secret Server with the Entrust nShield HSM. Secrets created in Delinea Secret Server will use encryption keys that are stored in the HSM.