Introduction
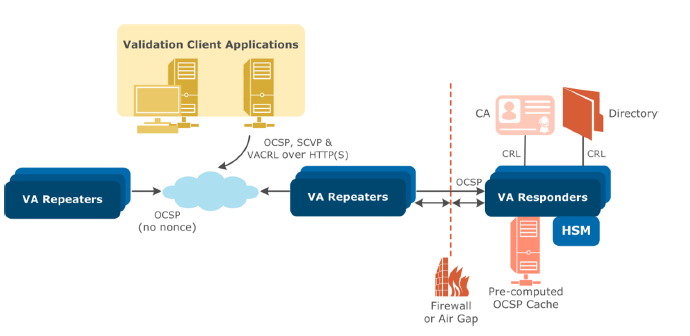
The Axway Validation Authority (VA) Server is an Online Certificate Status Protocol (OCSP) server that distributes certificate revocation information for certificates issued by any certification authority (CA). The VA Server ensures the integrity and validity of online transactions by validating digital certificates issued by a CA in real-time. The Entrust nShield Hardware Security Module (HSM) integrates with the Axway VA responder server through the nShield PKCS #11 cryptographic API to securely generate and store the OCSP response signing keys. The following image shows such an integration:
Requirements
The Axway VA installation requires either Microsoft Windows Server or Red Hat Enterprise Linux as the base operating system. CentOS systems should work similarly, though they are not tested. Obtain the installation package for Windows or Linux from Axway Support.
Reference the Axway Validation Authority Administrators Guide for product specific requirements.
Before starting this integration, review:
-
The documentation for the nShield Connect HSM.
-
The documentation and configuration process for Axway VA.
Before implementing nShield solutions:
-
Identify who will be the custodians of the administrator card set (ACS).
-
Obtain enough blank smart cards to create the ACS.
-
Define the Security World parameters. For details about the security implications of these parameters, see the nShield Security Manual.
| Entrust recommends allowing only unprivileged connections unless performing administrative tasks. |
Licensing
Configuring Axway VA requires importing a license file into the Axway VA administration web UI. Obtain the license file to configure Axway VA.
Product configurations
Entrust tested nShield HSM integration with Axway VA in the following configurations:
| Product | Version |
|---|---|
Axway Validation Authority |
v5.2 BN33837 UP202606 |
Windows |
Windows Server 2025 |
Red Hat Enterprise Linux |
release 10 |
HSM Hardware |
Connect XC and nShield 5C |
Supported features
Entrust tested nShield HSM integration with the following features:
| Softcard | Module | OCS | nSaaS |
|---|---|---|---|
Yes |
Yes |
Yes |
Not Tested |
Supported nShield hardware and software versions
Entrust tested with the following nShield hardware and software versions:
| nShield Hardware | nShield HSM Firmware | Security World Software |
|---|---|---|
Connect XC |
13.6.18 |
|
nShield 5c |
13.6.18 |
Supported nShield functionality
| Feature | Support |
|---|---|
Key Generation |
Yes |
Key Management |
Yes |
Key Import |
No |
Key Recovery |
Yes |
FIPS 140 Level 3 mode support for Connect XC |
Yes |
FIPS 140 Level 3 mode support for nShield 5c |
Yes |
Common Criteria mode support |
N/A |
1-of-N Operator Card Set |
Yes |
K-of-N Operator Card Set |
Yes |
Softcards |
Yes |
Module-only keys |
Yes |
Load Sharing |
Yes |
Failover |
Yes |