Deploy and configure the nShield HSM
All steps in this section are performed on the server hosting Secret Server.
Install the nShield Security World software
-
Sign in to the Vault Server using an account with administrator privileges.
-
Install the Security World software.
For detailed instructions, see the nShield Security World documentation. -
Add the Security World utilities path to the system path.
This path is typicallyC:\Program Files\nCipher\nfast\bin. -
Run the
enquiryutility to confirm that the Security World is inoperationalmode.C:\Users\Administrator>enquiry Server: enquiry reply flags none enquiry reply level Six serial number mode operational version 13.6.18 -
Open firewall port 9004 for the Entrust nShield HSM connections.
-
If using Remote Administration, open firewall port 9005 for the Entrust nShield Trusted Verification Device (TVD).
Install the Entrust nShield HSM
Install the nShield HSM. Condensed instructions are available in the Entrust TrustedCare Portal.
For detailed instructions see the Hardware install and setup guides.
Enroll the Entrust nShield HSM
-
Inform the HSM of the location of the Vault Server.
For instructions, see Configuring the nShield HSM to use the client.
If you are using a high-availability setup, repeat the client configuration for each HSM.
-
Enroll the Vault Server as a client of the HSM.
For instructions, see Configuring client computers to use the nShield HSM.
If you are using a high-availability setup, repeat the enrollment for each HSM.
-
Run the
enquiryutility to confirm that the HSM is inoperationalmode.C:\Users\Administrator>enquiry Server: enquiry reply flags none enquiry reply level Six serial number 6A74-1261-7843 810B-03E0-D947 mode operational version 13.6.18 ... Module #1: enquiry reply flags UnprivOnly enquiry reply level Six serial number 6A74-1261-7843 mode operational version 13.4.5 ... Module #2: enquiry reply flags UnprivOnly enquiry reply level Six serial number 810B-03E0-D947 mode operational version 12.72.4
Create a security world
-
Create a new Security World, if one does not already exist, or copy an existing one.
Follow your organization’s security policy for this. For more information see Create a new Security World.
ACS cards cannot be duplicated after the Security World is created. You may want to create extras in case of a card failure or a lost card. -
Confirm the Security World is in a
Usablestate with thenfkminfoutility.C:\Users\Administrator>nfkminfo World generation 2 state 0x3737000c Initialised Usable ... ... Module #1 generation 2 state 0x2 Usable ... Module #2 generation 2 state 0x2 Usable
Select the protection method
The following protection methods are available to authorize access to Secret Server keys protected by the HSM.
-
An Operator Card Set (OCS) is a set of smartcards that are presented to the physical smartcard reader of an HSM. For more information on OCS use, properties, and K-of-N values, see Operator Card Sets (OCS).
-
Softcards are logical tokens (passphrases) that protect the key and authorize its use. For more information on softcard use, see Softcards.
-
Module protected keys are simply protected by a module key. For more information on module protection, see Module protection.
Follow your organization’s security policy to select an authorization access method.
Depending on the protection method select, you may need to define some environment variables.
You have the option to set these environment variables with the Windows set command, or edit file C:\Program Files\nCipher\nfast\cknfastrc.
The Windows set command is preferred.
As reference, all environment variables are listed in nShield PKCS #11 library environment variables.
Enable softcard protection:
C:\Users\Administrator.INTEROP>set CKNFAST_LOADSHARING=1
Enable module protection:
C:\Users\Administrator.INTEROP>set CKNFAST_FAKE_ACCELERATOR_LOGIN=1
Sample C:\Program Files\nCipher\nfast\cknfastrc file:
# Enable Softcard protection
CKNFAST_LOADSHARING=1

# Enable Module protection
CKNFAST_FAKE_ACCELERATOR_LOGIN=1

# OCS Preload file location
# Un-comment the next line ONLY in using preload
#NFAST_NFKM_TOKENSFILE="C:\Program Files\nCipher\nfast\preloadtoken"
Create the OCS
The OCS quorum and passphrase must be set as shown next.
| Feature | CNG Cryptography Provider | PKCS #11 API |
|---|---|---|
Quorum K |
1 |
1 |
Passphrase |
None. Left blank |
<passphrase> |
Recovering from a power failure requires the OCS to be inserted in the HSM or the TVD.
-
Ensure file
/opt/nfast/kmdata/config/cardlistcontains the serial number of the card(s) to be presented or an asterisk wildcard the use of any card. -
Open a command window as
Administrator. -
Create the OCS as described in Create Operator Card Sets (OCSs).
Follow your organization’s security policy for the values of K/N, where K=1 as mentioned above. Use the same passphrase (left blank with CNG) for all the OCS cards in the set (one for each person with access privilege, plus spares).
In the example below,
slot 2, remote via TVD, was used to present the card in this integration.The
-p(persistent) option makes the authentication persist after you remove OCS card from the HSM front panel slot or from the TVD.After an OCS card set has been created, the cards cannot be duplicated. # createocs -m1 -s2 -N testOCSnopassphrase -Q 1/1
-
Verify that the OCS was created.
C:\Users\Administrator.INTEROP>nfkminfo -c
Cardset list - 2 cardsets:  (P)ersistent/(N)ot, (R)emoteable/(L)ocal-only
 Operator logical token hash               k/n timeout  name
 7aaf758bc6790206198ea5218040d4faa09f035f  1/5  none-NL testOCSnopassphrase
 edb3d45a28e5a6b22b033684ce589d9e198272c2  1/5  none-NL testOCS
The
rocsutility also shows the OCS created.C:\Users\Administrator.INTEROP>rocs `rocs' key recovery tool Useful commands: `help', `help intro', `quit'. rocs> list cardset No. Name Keys (recov) Sharing 1 testOCSnopassphrase 0 (0) 1 of 5 2 testOCS 1 (1) 1 of 5 rocs> exit
Create the softcard
-
Enable softcard protection as described in Select the protection method.
-
Open a command window as an administrator.
-
Create the softcard as described in Create softcards.
For example
# ppmk -n testSC -
Verify the softcard.
# nfkminfo -s
SoftCard summary - 1 softcards:
 Operator logical token hash               name
 9252345678923456234567897bde3753d24e7744  testSC
The
rocsutility also shows the new softcard.# rocs `rocs' key recovery tool Useful commands: `help', `help intro', `quit'. rocs> list cards No. Name Keys (recov) Sharing 1 testOCS 0 (0) 1 of 5 2 testSC 0 (0) (softcard) rocs> quit
Automatically start the nShield service agent at startup
-
Create a shortcut of
C:\Program Files\nCipher\nfast\bin\nShield_service_agent.exeand place temporarily on the desktop. -
Select the Windows key + R, type shell:startup. Then select OK.
-
Move the shortcut to the Startup folder.
-
Reboot.
-
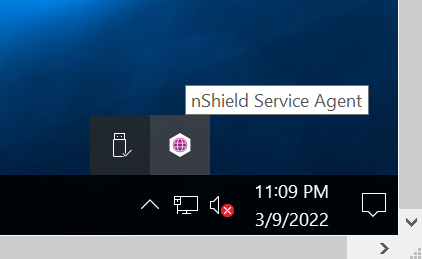
Notice the nShield service agent icon shown below.