Install and configure directory service
Install directory service
The Certificate Authority requires a directory service that supports LDAP (Lightweight Directory Access Protocol) or a third-party LDAP-compliant X.500 directory. A remote OpenLDAP directory service with a self-signed certificate was used in this integration. See Product Support Center for Authority for a list of supported directory services.
-
Install the required LDAP client tools on the Certificate Authority server.
-
In the firewall rules on the server hosting the directory service, allow inbound traffic from the Certificate Authority server on port 389.
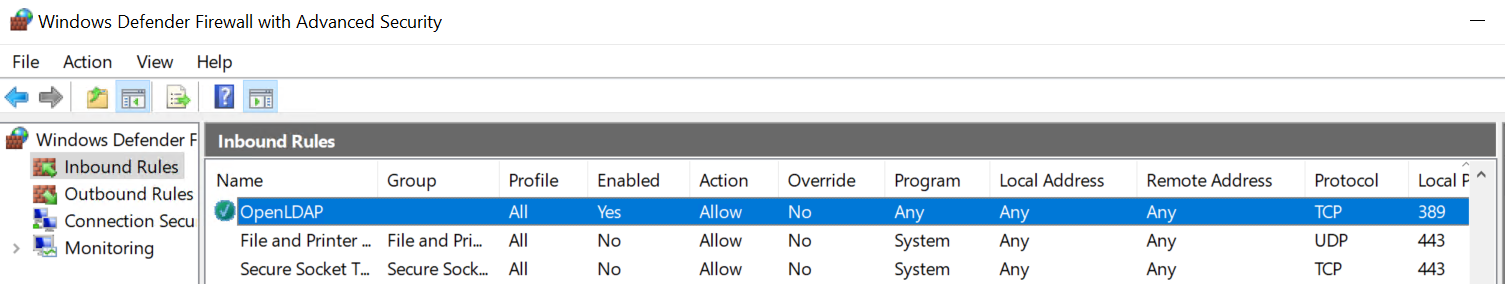
Configure directory service
The Certificate Authority directory schema configuration is described in Entrust Certificate Authority.
-
Implement the configuration corresponding to your directory service.
The following directory service parameters are used in this integration:
-
Top Level DN:
dc=entrustsm,dc=local -
CA Directory Location:
ou=CAentry,dc=entrustsm,dc=local -
Directory Administrator:
cn=EntrustAdmin,ou=CAentry,dc=entrustsm,dc=local -
First Officer:
cn=FirstOfficer,ou=CAentry,dc=entrustsm,dc=local
-
-
Test access to the directory service:
C:\Users\Administrator>C:\OpenLDAP\ClientTools\ldapsearch -x -H ldap://<directory_services_server_IP_or_Name> -D "cn=EntrustAdmin,ou=CAentry,dc=entrustsm,dc=local" -b "cn=EntrustAdmin,ou=CAentry,dc=entrustsm,dc=local" -s sub -W
Enter LDAP Password: *******
# extended LDIF
#
# LDAPv3
# base <cn=EntrustAdmin,ou=CAentry,dc=entrustsm,dc=local> with scope subtree
# filter: (objectclass=*)
# requesting: ALL
#

# EntrustAdmin, CAentry, entrustsm.local
dn: cn=EntrustAdmin,ou=CAentry,dc=entrustsm,dc=local
objectClass: top
objectClass: person
objectClass: organizationalPerson
objectClass: inetOrgPerson
uid: entrustadmin
sn: Administrator
userPassword: **[redacted]**
description: Certificate Authority Directory Administrator
cn: EntrustAdmin

# search result
search: 2
result: 0 Success

# numResponses: 2
# numEntries: 1