Integrate the Entrust Cryptographic Security Platform PKI Hub and the Entrust nShield HSM
Make the Entrust Cryptographic Security Platform PKI Hub server a client of the HSM
-
Using the HSM front panel, add the IP address of the Entrust Cryptographic Security Platform PKI Hub server as a client of the HSM.
-
Present the OCS card from Install and configure the Entrust nShield HSM to the HSM through the front panel card reader.
Configure the Entrust Cryptographic Security Platform PKI Hub
-
Log in to the Entrust Cryptographic Security Platform PKI Hub Management Console web interface as explained in Starting up the Management Console in the Cryptographic Security Platform PKI Hub documentation.
-
In the content pane, under Certificate Authorities, select Manage Solution.
-
Leave Import configuration set to its default off position.
-
Set Enable Advanced Configuration to Yes.
-
Select Next.
-
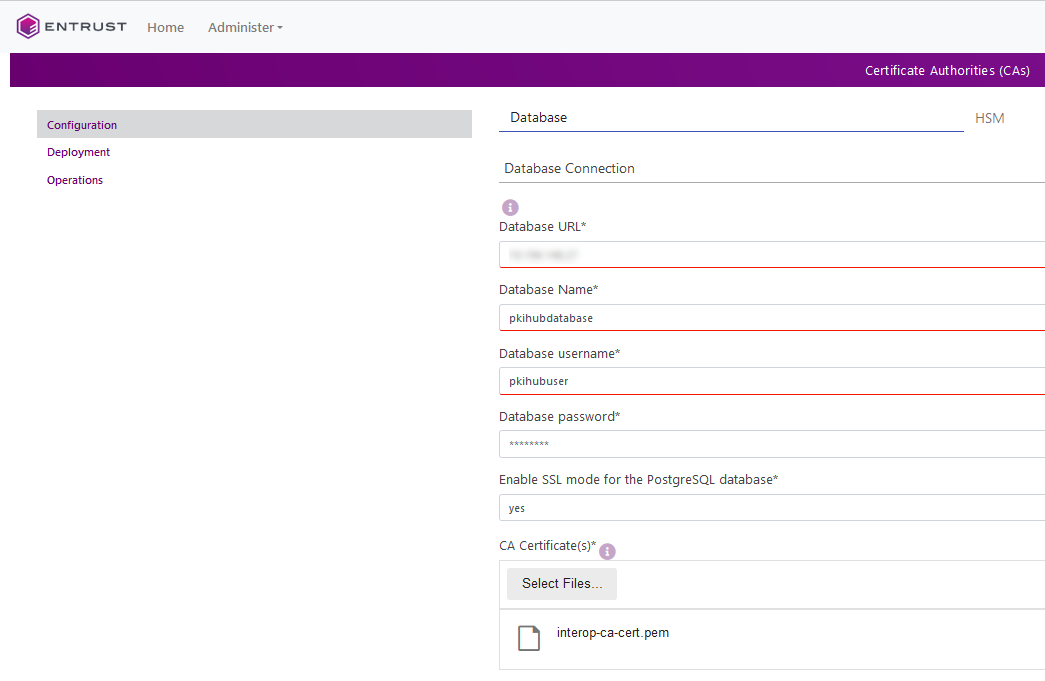
In the Database tab, enter the database information described in Deploy Entrust Cryptographic Security Platform PKI Hub, then select Next.
You must create a separate database for the solution. Do not use the same database used to deploy the PKI Hub cluster. For example:
-
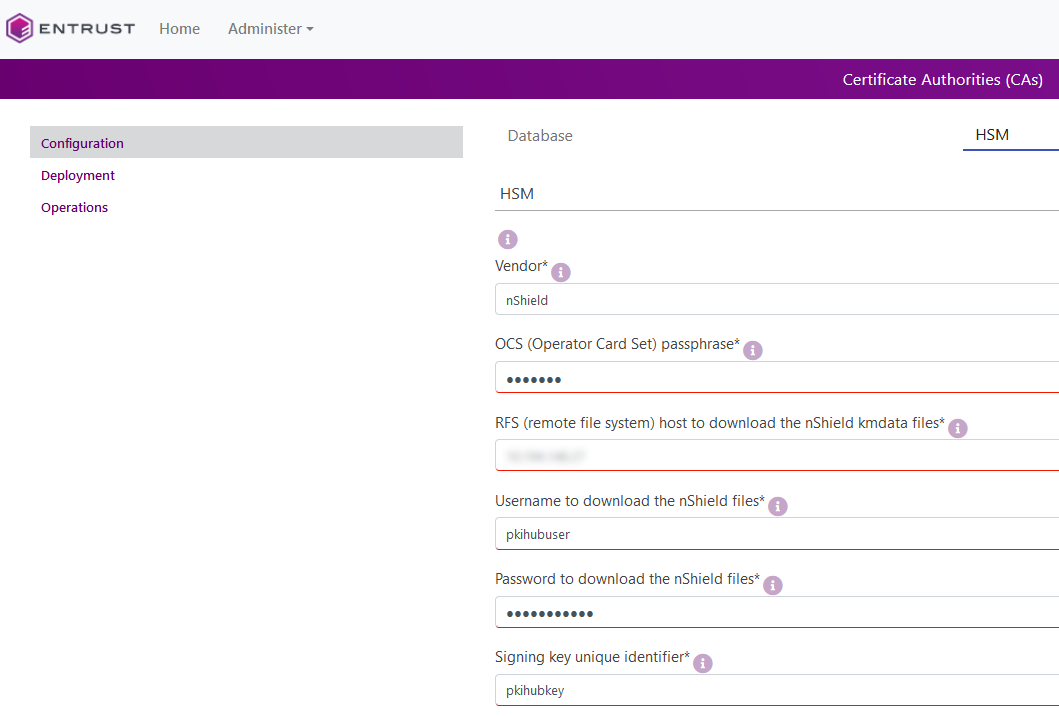
In the HSM tab, enter the HSM information.
-
For Vendor: Select nShield.
-
For OCS (Operator Card Set) passphrase: Enter the passphrase for the OCS card being used for the integration.
-
For The nShield kmdata tar file:
Create a tar file containing the HSM’s Key Management data directory (
kmdata) and upload it here. The file should contain the OCS card files created for the integration. Run this shell command on the server where the HSM was configured and thekmdatadirectory is located.% sudo tar -cf x.tar -C /opt/nfast kmdata.Then copy
kmdata.tarto your host so you can upload it here. -
Select Next.
For example:
-
-
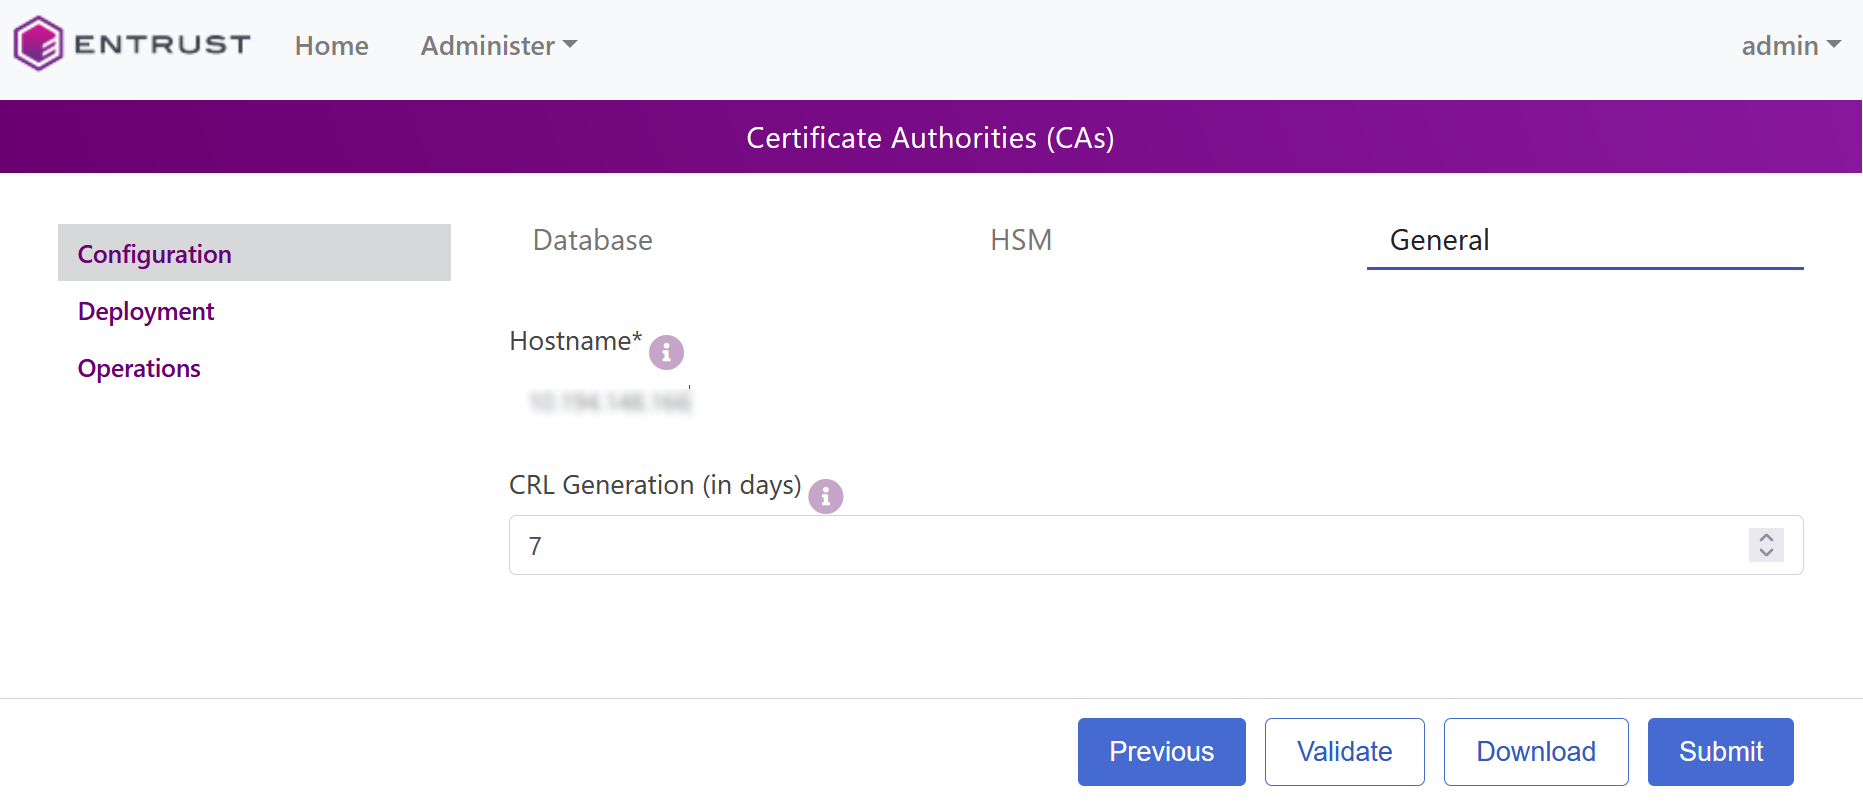
In the General tab, enter the Entrust Cryptographic Security Platform PKI Hub hostname or IP.
For example:
-
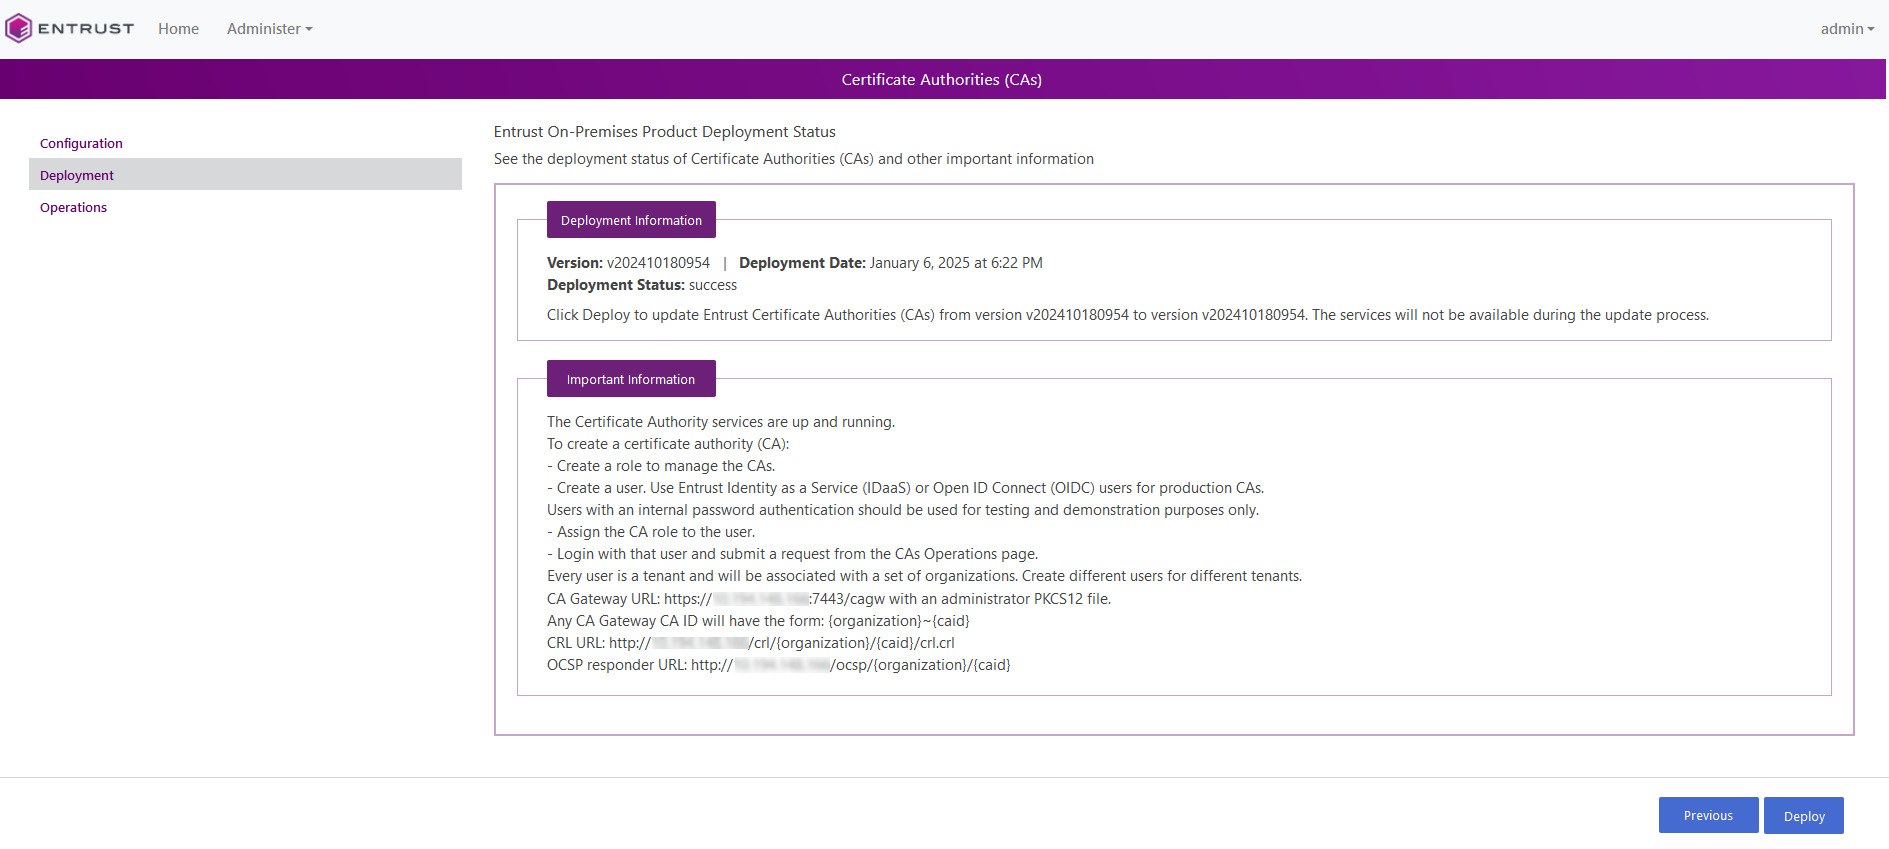
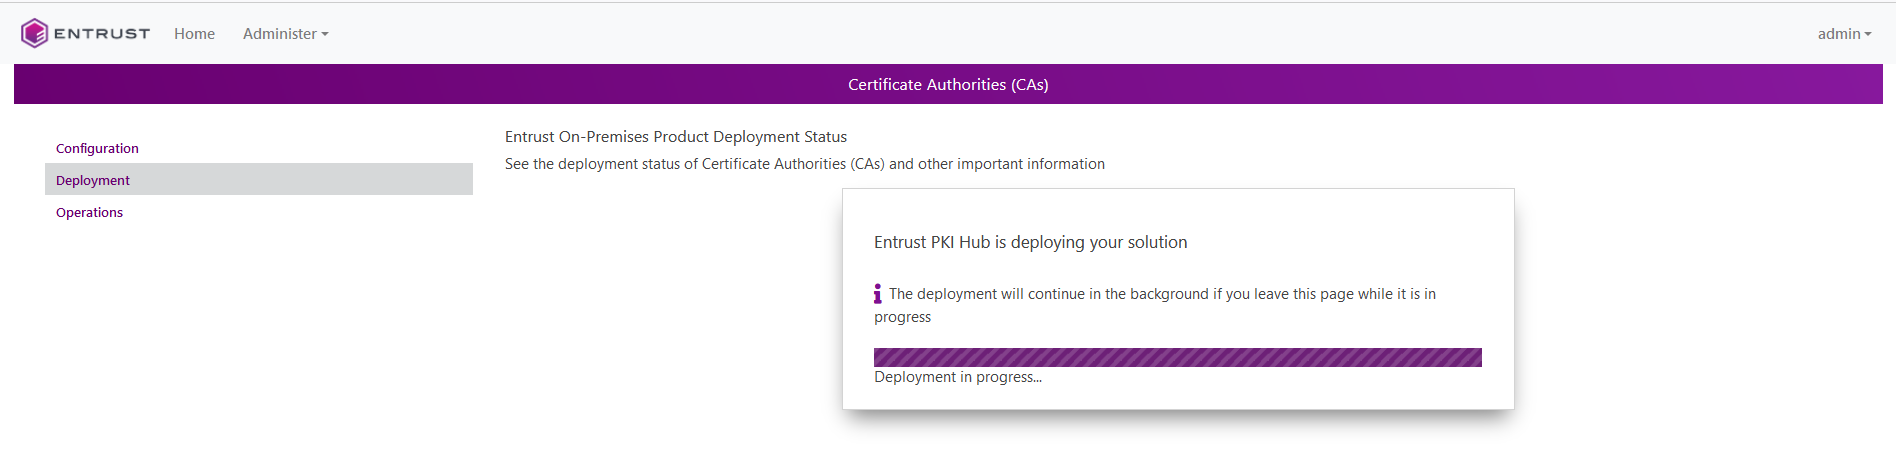
Select Submit. If everything is accepted, the console displays the Deployment page.
-
Select Deploy, then, in the Confirmation pop-up window, select Yes. After a few minutes, the integration with the Entrust nShield HSM is complete.
For example: